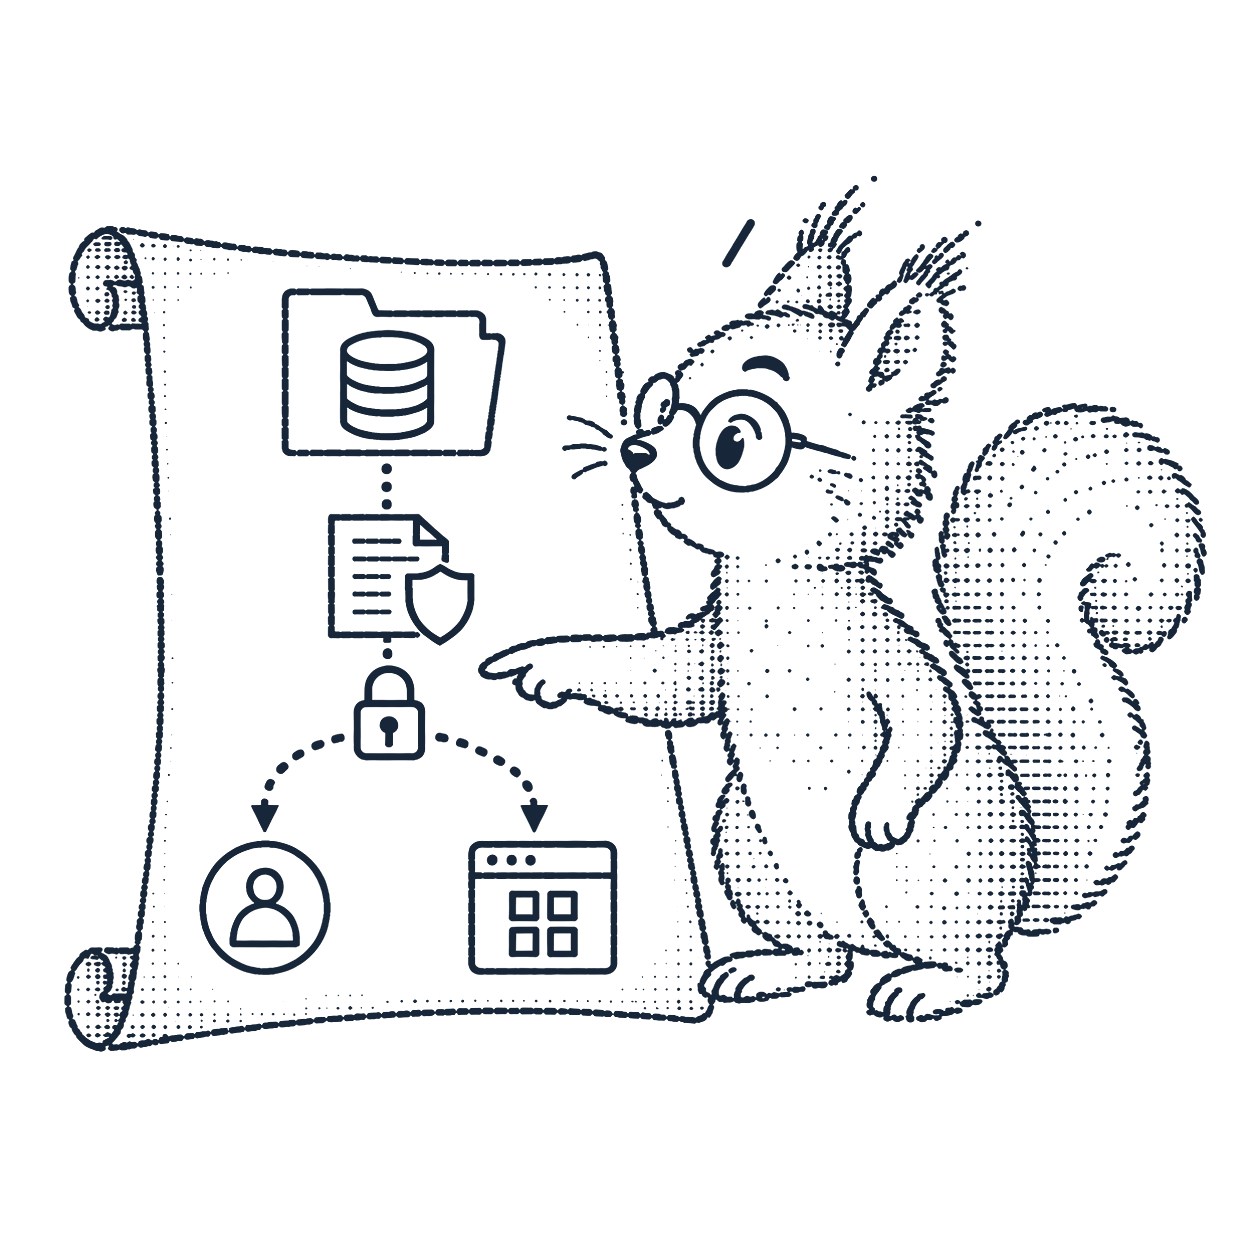
One completed assessment for audit readiness and better security decisions. We start with how your business operates, your existing controls and the risks they address. We examine the protections those controls should provide, including dependencies they share.
See what holds up, what needs attention and what remains unproven, with evidence prepared for audit. Built around your existing controls, evidence and workflows.
Start with the customer’s environment and the paths that could leave access open after departure.
The control
Withdraw central, application and session access within four hours.
02 / Éprouver
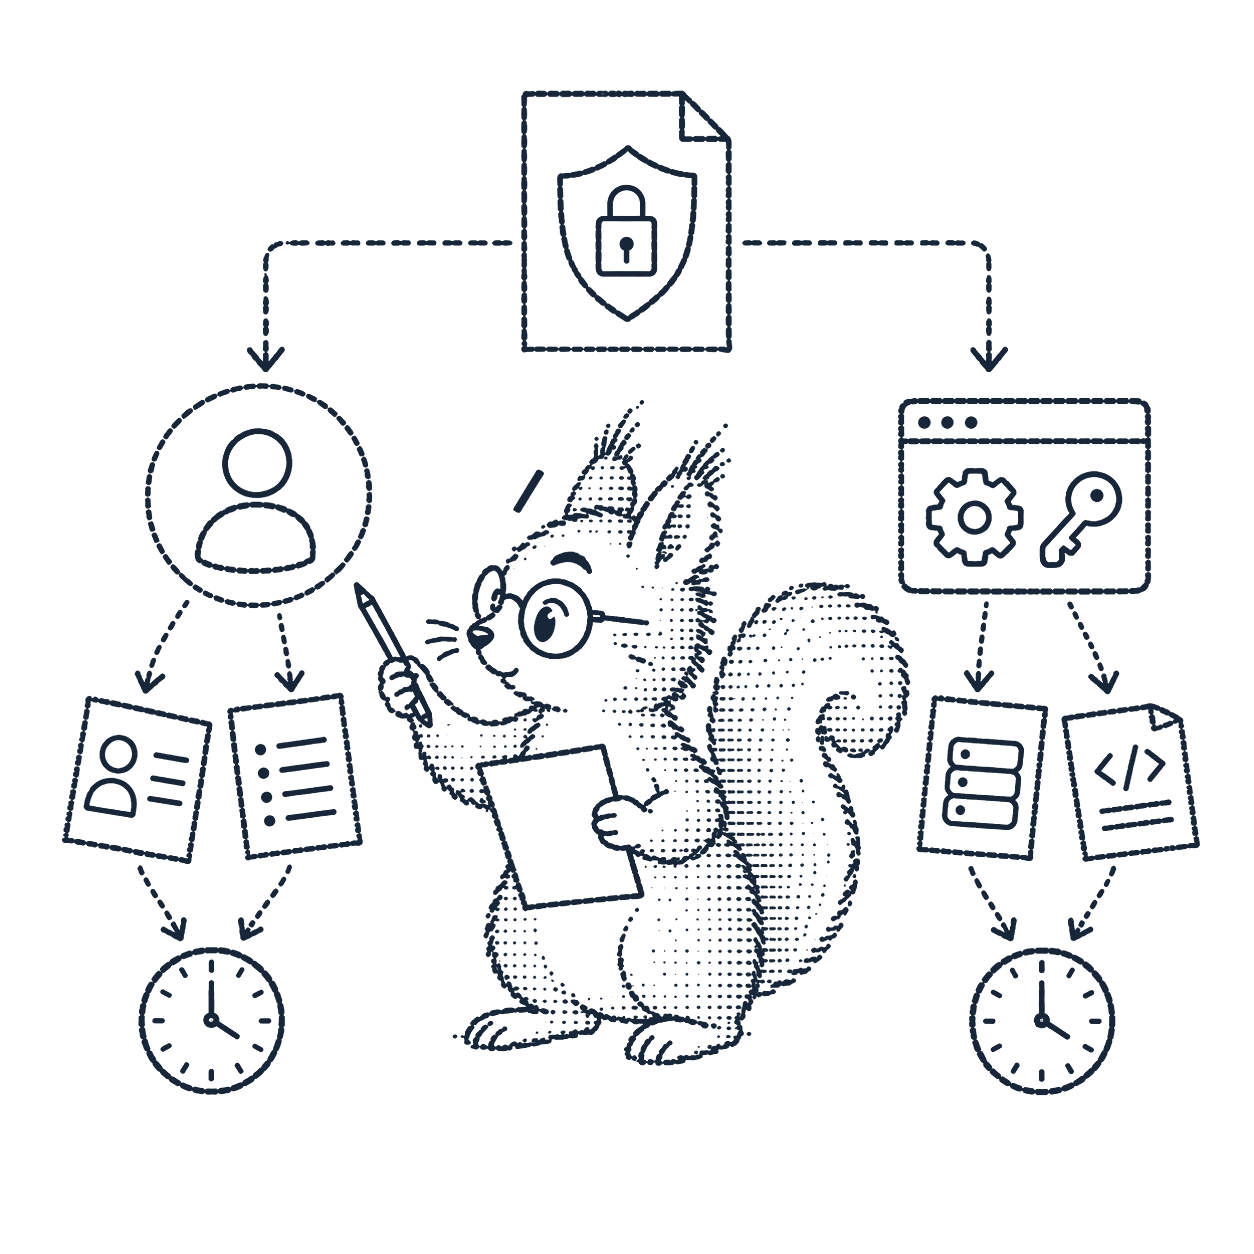
One control. Separate examinations.
Examine central identity and application access against their own deciding records.
What the records show
Central disablement: 10–15 minutes. One application withdrawal: after the deadline.
03 / Évaluer
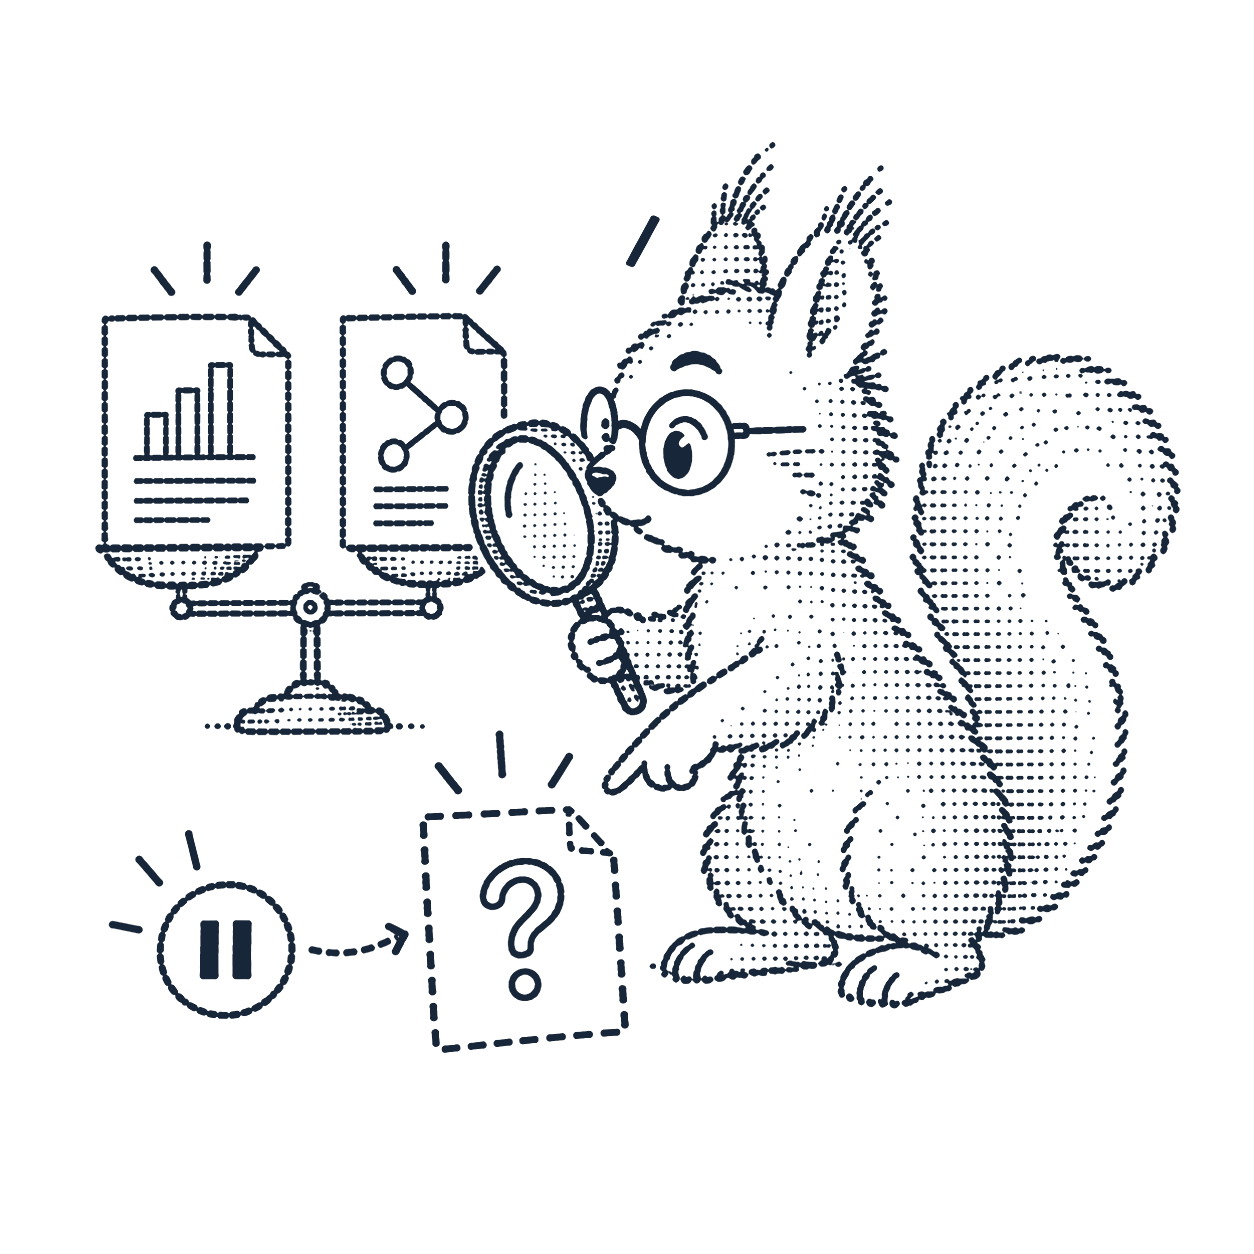
What does the evidence establish?
Challenge both the examination’s coverage and the conclusions drawn from it.
Review remains on hold
Missing access history remains unresolved. Late withdrawal does not establish an attacker or data theft.
04 / Éclairer
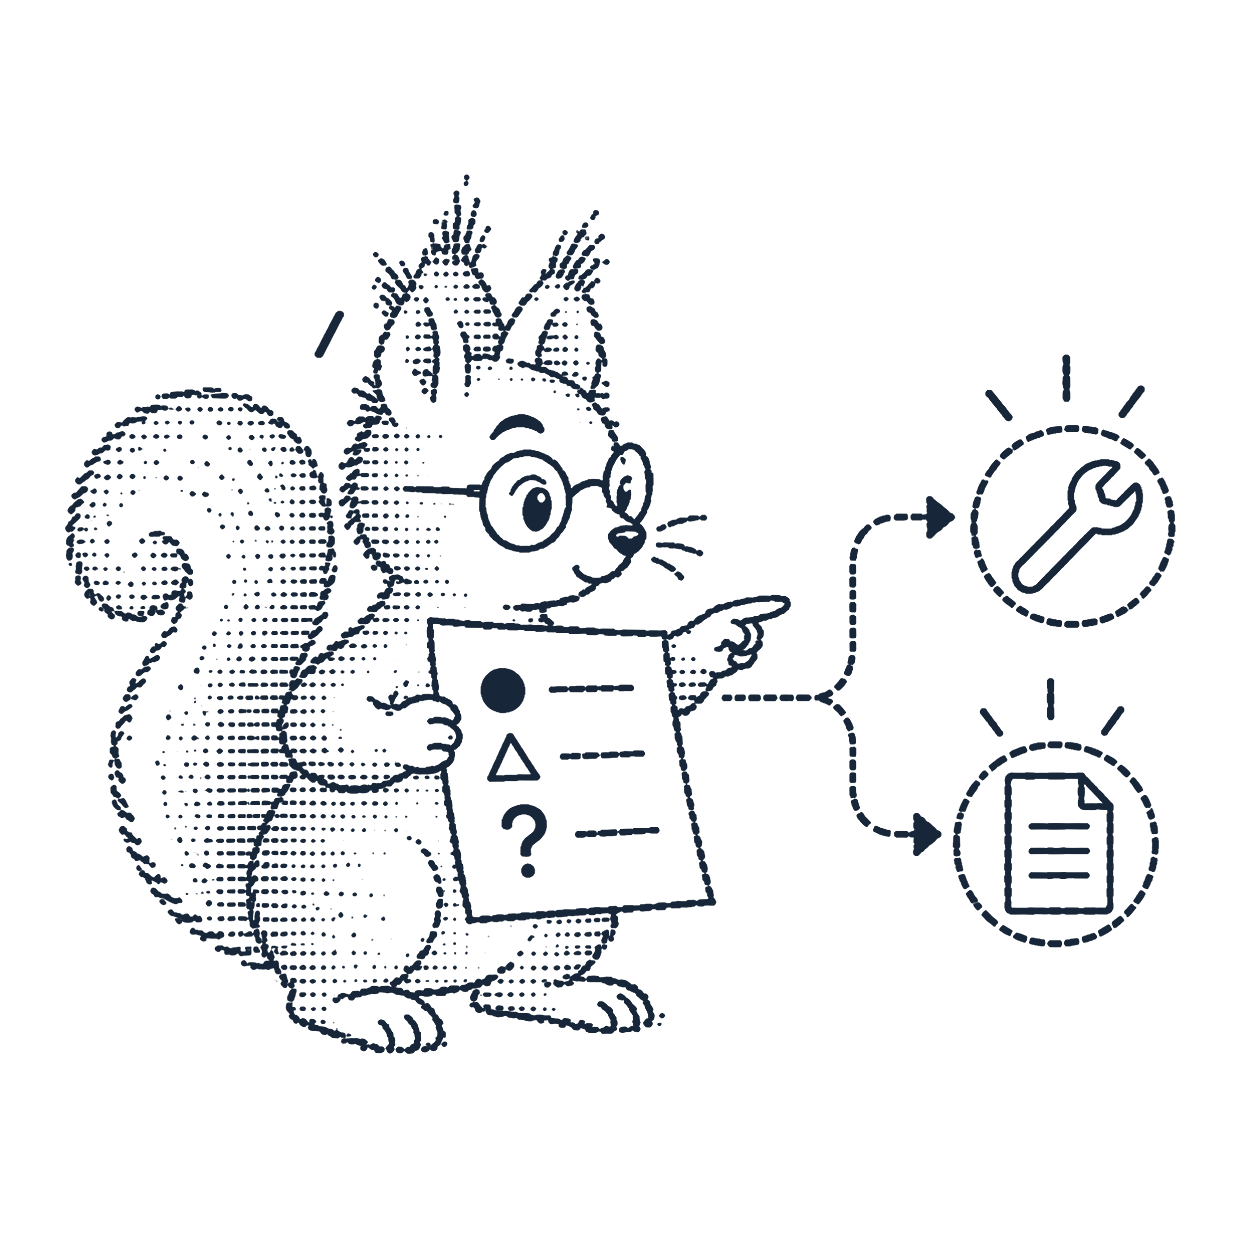
Make the next action clear.
Separate the established finding from the evidence still needed for reassessment.
The next step
Address the late application withdrawal and obtain the missing access history. This result has not been released.
This is one examination within an assessment. The engagement covers the full agreed audit scope; risk-driven depth does not remove required work.
Method illustration using one retained fictional result: three departures, archive-prod, June 2026. Scripted review, not independent professional validation. This run used fixed procedures; it does not demonstrate the newer contextual-planning implementation.
Stipulated configuration checks enforce MFA on the standard workforce route.
ILL-P02 / Recovery & exceptions
Examination
partial
Outcome
unresolved
Evidence
incomplete
Recovery-route exception records are incomplete; alternate entry is unresolved.
IDENTITY SCENARIOSession managementpartial
ILL-ASMT-01 / ILL-C02
ILL-P03 / Central session revocation
Examination
examined
Outcome
supported
Evidence
sufficient for this test
Stipulated revocation checks invalidate central sessions.
ILL-P04 / Application token revocation
Examination
partial
Outcome
unresolved
Evidence
incomplete
Token inventory and revocation history are incomplete.
IDENTITY SCENARIOOffboardingpartial
ILL-ASMT-01 / ILL-C03
ILL-P05 / Identity disablement
Examination
examined
Outcome
supported
Evidence
sufficient for this test
Stipulated departure checks meet the disablement criterion.
ILL-P06 / Independent application access
Examination
partial
Outcome
unresolved
Evidence
incomplete
Local-account departure reconciliation remains incomplete. Relevant only if the compromised identity belongs to a leaver.
IDENTITY SCENARIOPrivileged accessexamined
ILL-ASMT-01 / ILL-C04
ILL-P07 / Elevation approval
Examination
examined
Outcome
supported
Evidence
sufficient for this test
Stipulated elevation records contain the required approvals.
ILL-P08 / Standing privilege boundaries
Examination
examined
Outcome
failure
Evidence
sufficient for this test
The stipulated support role retains an export-administration permission contrary to its approved role definition.
IDENTITY SCENARIOSensitive-data accesspartial
ILL-ASMT-01 / ILL-C05
ILL-P09 / Standard effective permissions
Examination
examined
Outcome
supported
Evidence
sufficient for this test
Stipulated standard-route checks enforce the approved data-access boundary.
ILL-P10 / Alternate API access
Examination
not examined
Outcome
undetermined
Evidence
not assessed
The alternate API route has not been examined.
IDENTITY SCENARIOExport restrictionspartial
ILL-ASMT-01 / ILL-C06
ILL-P11 / Export authorization
Examination
examined
Outcome
failure
Evidence
sufficient for this test
The illustrative supplied export-test record describes a support-role export proceeding without required approval. This examination inspects the record; Épreuve performs no active export test.
ILL-P12 / Destination restrictions
Examination
not examined
Outcome
undetermined
Evidence
not assessed
Export destination enforcement has not been examined.
IDENTITY SCENARIOLogging & responsepartial
ILL-ASMT-01 / ILL-C07
ILL-P13 / Export event coverage
Examination
partial
Outcome
unresolved
Evidence
incomplete
The export-event record is incomplete; detection coverage is unresolved.
ILL-P14 / Alert-to-response exercise
Examination
not examined
Outcome
undetermined
Evidence
not assessed
No response exercise has been examined.
OTHER SCOPEBackup recoveryexamined
ILL-ASMT-01 / ILL-C08
ILL-P15 / Restore execution
Examination
examined
Outcome
supported
Evidence
sufficient for this test
Stipulated restore checks meet the declared recovery criterion.
ILL-P16 / Recovery validation
Examination
examined
Outcome
supported
Evidence
sufficient for this test
Stipulated restored-record comparisons match the sampled originals.
OTHER SCOPEChange managementpartial
ILL-ASMT-01 / ILL-C09
ILL-P17 / Production approval
Examination
examined
Outcome
supported
Evidence
sufficient for this test
Stipulated sampled production changes contain approval records.
ILL-P18 / Emergency-change review
Examination
partial
Outcome
unresolved
Evidence
incomplete
Emergency-change population reconciliation is incomplete.
02 / FOR SECURITY LEADERSHIP
Follow the risk across controls.
Could a compromised workforce identity reach and extract sensitive customer data?
This scenario is one view into the scope. The branches are hypotheses to examine, not a demonstrated exploit chain.
IDENTITY EXPOSURE / ILLUSTRATION02
Inspect the contributing controls
ILL-SCN-01 · authored assessment states
01 / Obtain access
Stolen credentials still face authentication. A stolen session is a separate entry route.
The support role is assumed to be unable to export without separate approval. The illustrated permission and export-record findings challenge that assumption. Prioritize restoring the role boundary and approval requirement.
Not examined: alternate API access, destination restrictions and the response exercise. Evidence incomplete: recovery routes, application tokens, application accounts and export-event coverage.
Complete the outstanding examinations and obtain the missing records before drawing a wider conclusion. Component failures do not establish a complete attack path or data theft.
✓ Supported · ! Failure in this illustration · ? Open question
03 / FOR AUDIT
Inspect the basis of the conclusion.
Start with assessment scope and coverage. Follow a finding into its criterion, procedure, records and review determination.
ASSESSMENT RECORD03
Scope & examination
ILLUSTRATIVE NOT ISSUED
1–30 September 2026 Workforce IdP, customer-vault and the export service
10 examined5 partial3 not examined
01
Declared scope
Nine controls across identity protection, backup recovery and change management.
02
Review held
Application accounts, recovery records and export-event coverage remain unresolved.
Population, accuracy and scope notes
ILL-ASMT-01 · illustrative inventories contain 12 workforce identities and four role definitions. Workforce and IdP lists reconcile; independently managed application accounts remain unresolved.
Two sampled role assignments agree with their source records. This does not establish the accuracy of every inventory field. Seven controls relate to the identity scenario; backup recovery and change management complete the declared scope.
Inspect the export finding
ILL-P11 · export authorization
Criterion
Every support-role export requires approval by a separate authorized owner before execution.
Period & population
1–30 September 2026. Four illustrative role definitions; this examination selects the support role and one supplied export-test record. It is not a census of historical exports.
Procedure
Compare the supplied support-role permission record with its approved definition. Inspect the supplied export-test record for execution, approval and role details. Épreuve performs no export attempt in this example.
Illustrative evidence
ILL-E01 role inventory; ILL-E02 approved role definitions; ILL-E03 supplied export-test record. These IDs describe authored fixtures, not collected customer records.
Stipulated observation
The illustrative supplied record describes a support-role export proceeding without the required approval. The record is assumed authentic and sufficient for this selected examination only; those assumptions require validation in a real assessment.
Reviewer determination
Proposed failure for ILL-P11; accountable review pending. No real reviewer has approved this illustration. Overall review remains held.
Separate reproducible example / retained D2 run
Alder Works, June 2026, archive-prod. This earlier offboarding fixture is a different case and period. Its results are not evidence for Northstar Labs or this identity scenario.
Run risk-run-bd1b55121121. Release held. Scripted synthetic review, not independent professional approval.
Its reconciled departure population does not establish enterprise completeness. Source authority is stipulated; the digest identifies file bytes, not information accuracy.
Northstar Labs is an authored illustration of assessment outputs. It does not demonstrate executed examinations, independent review or dynamic test planning. The separate retained D2 example has its own provenance.
Bring your audit timeline, full audit scope and the security questions the assessment should answer. The first conversation establishes fit, evidence access and a practical scope.
Proposed service in development. Discovery conversations are open.